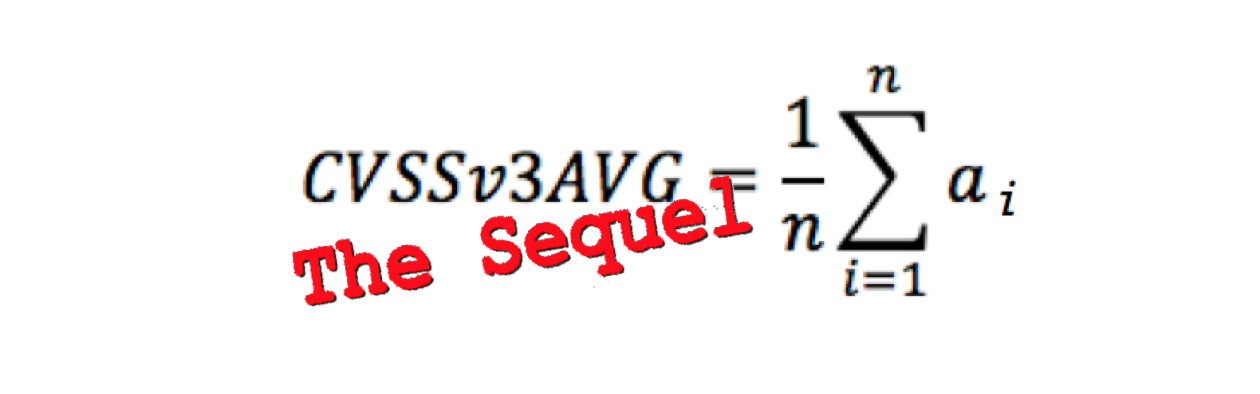Omar Santos is a Distinguished Engineer at Cisco focusing on artificial intelligence (AI) security, cybersecurity research, incident response, and vulnerability disclosure. He is the co-chair of the Coalition for Secure AI (CoSAI) and a board member of the OASIS Open standards organization. Omar is also the chair of the OpenEoX and the Common Security Advisory Framework (CSAF) technical committee. His work led the creation of the CSAF ISO standard.
Omar's collaborative efforts extend to numerous organizations, including the Forum of Incident Response and Security Teams (FIRST) and the Industry Consortium for Advancement of Security on the Internet (ICASI). Omar is the co-chair of the FIRST PSIRT Special Interest Group (SIG) and was the lead of the DEF CON Red Team Village for several years.
Omar is the author of over 25 books, 21 video courses, and over 50 academic research papers. Omar is a renowned expert in ethical hacking, vulnerability research, incident response, and AI security. Omar's work in cybersecurity is also recognized through multiple granted patents. Prior to Cisco, Omar served in the United States Marines focusing on the deployment, testing, and maintenance of Command, Control, Communications, Computer, and Intelligence (C4I) systems.
The Cisco Product Security Incident Response Team (PSIRT) is now scoring all security advisories addressing security vulnerabilities that affect Cisco products and multivendor vulnerability alerts using the Common Vulnerability Scoring System version 3 (CVSSv3). The stakeholders at the Forum of Incident Response and Security Teams (FIRST) have done a great job in this new version […]
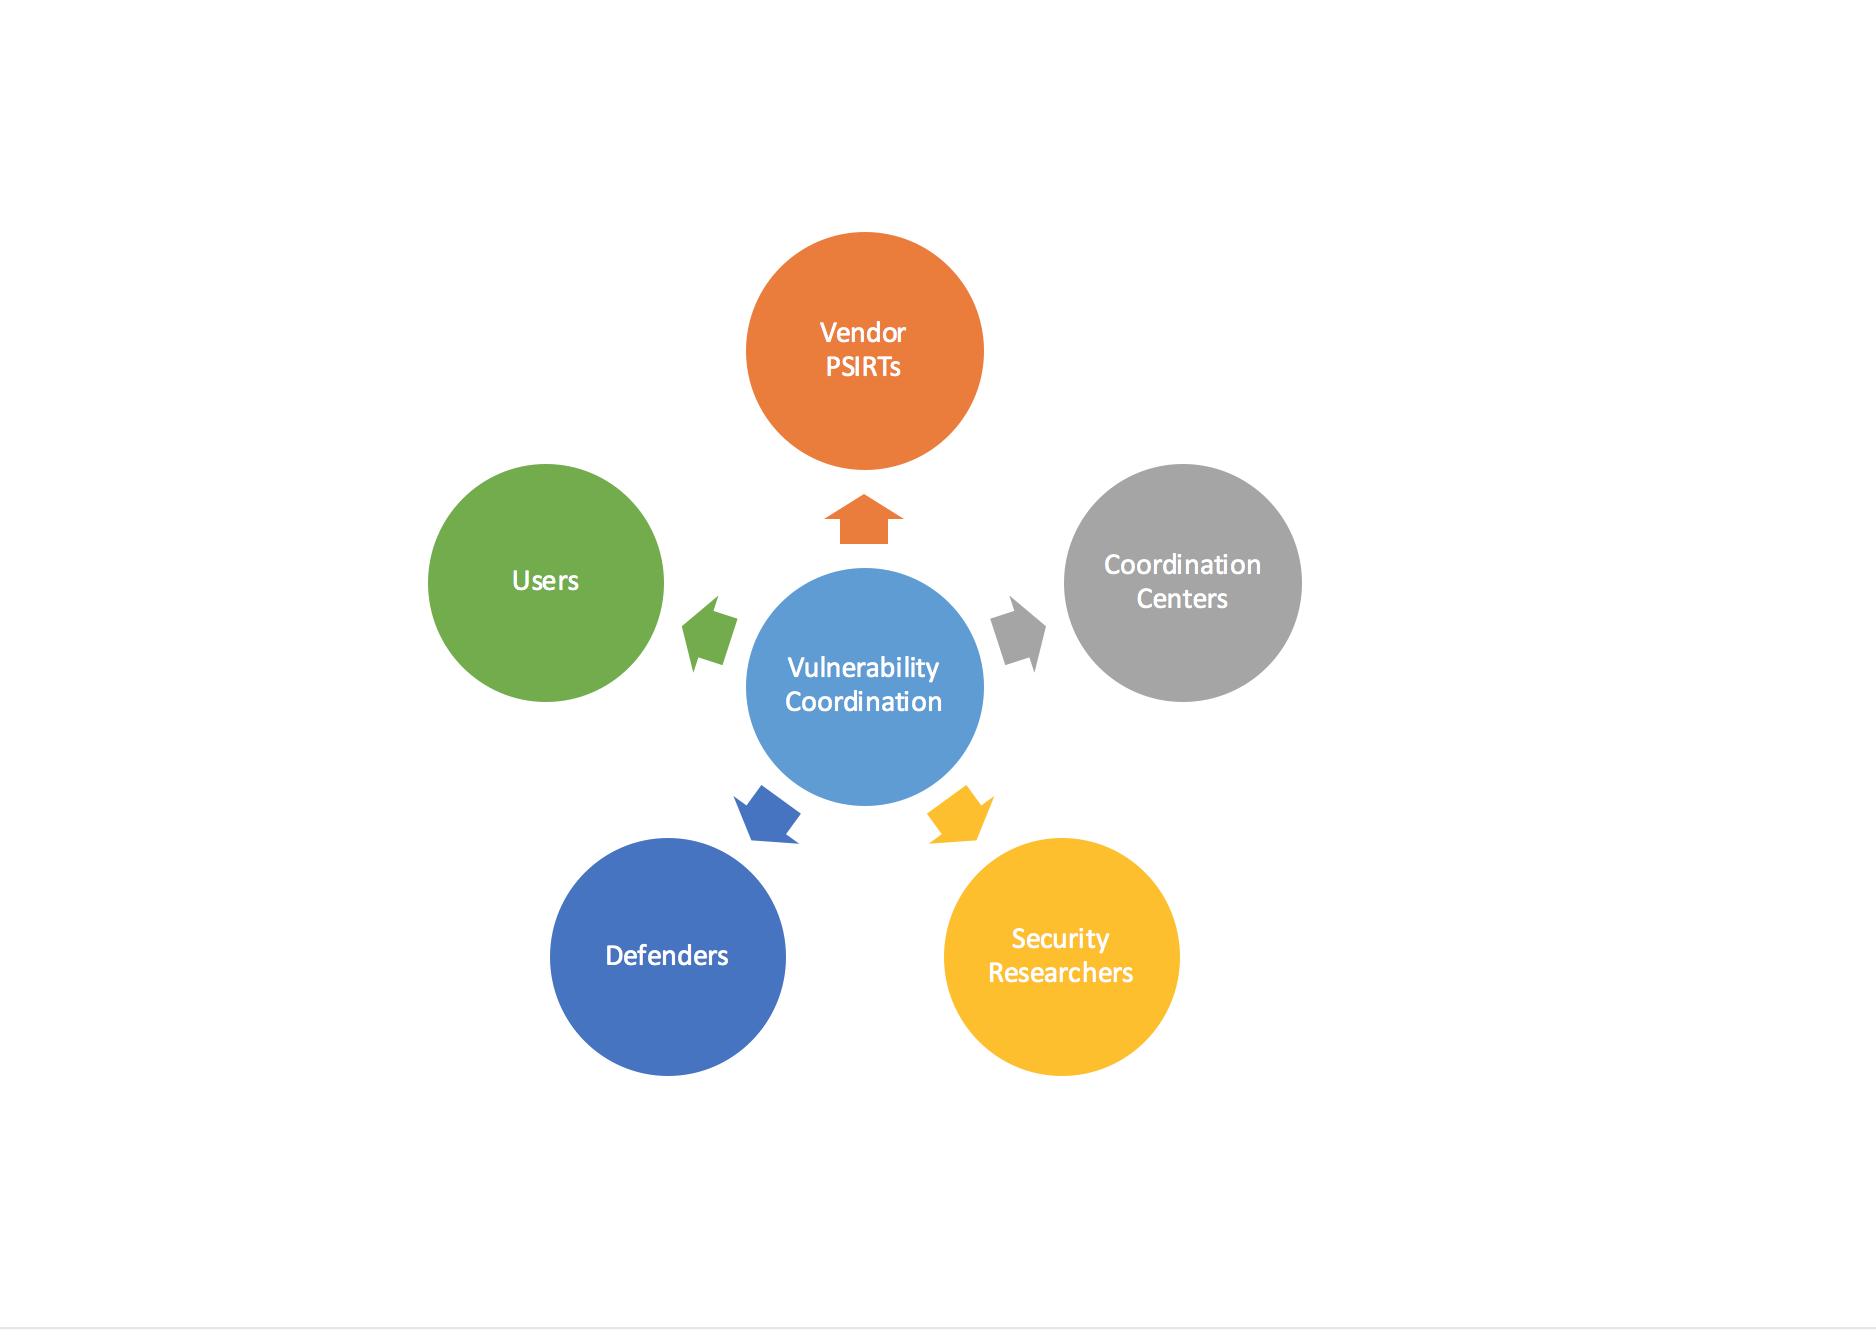
Recent cyber attacks on organizations around the world have demonstrated the need for consistency in managing security vulnerabilities. To answer that demand, the Industry Consortium for the Advancement of Security on the Internet (ICASI) and the Forum of Incident Response and Security Teams (FIRST) created the FIRST Vulnerability Coordination Special Interest Group (SIG). This is […]
Back in April, I wrote a blog post about the new version of the Common Vulnerability Scoring System (CVSS). The changes made for CVSSv3 addressed some of the challenges that existed in CVSSv2. For example, CVSSv3 analyzes the scope of a vulnerability and identifies the privileges an attacker needs to exploit it. The CVSSv3 enhancements […]
During the last few years we have witnessed how the cyber security threat landscape has evolved. The emergence of the Internet of Things combined with recent events have profoundly changed how we protect our systems and people, and drive us to think about new approaches for vendors to disclose security vulnerabilities to customers and consumers. […]
UPDATE April 20, 2017 Cisco continues to evaluate potential implications of the activities and information posted publicly by the Shadow Brokers Group. We launched an investigation to analyze the new files posted on April 14th, 2017, and so far have not found any new vulnerabilities or exploits that affect Cisco products and services. Cisco PSIRT will […]
The Common Vulnerability Scoring System (CVSS), which is used by many in the industry as a standard way to assess and score security vulnerabilities, is evolving to a new version known as CVSSv3. These changes addressed some of the challenges that existed in CVSSv2; CVSSv3 analyzes the scope of a vulnerability and identifies the privileges […]
In October, we announced details about Cisco PSIRT’s new and improved security vulnerability disclosure format. Our Chief Security and Trust Officer, John Stewart, also revealed that Cisco will launch an application programming interface (API) that empowers customers to customize Cisco vulnerability information and publications. Today, we have officially launched the Cisco PSIRT openVuln API and it is available […]
Cisco is committed to protecting customers by sharing critical security-related information in different formats. Guided by customer feedback, Cisco’s Product Security Incident Response Team (PSIRT) is seeking ways to improve how we communicate information about Cisco product vulnerabilities to our Customers and Partners. As John Stewart mentioned on his blog post, the Cisco PSIRT has launched a […]
The security of our customers is critical, and when needed, we pull out all stops to protect them. Cisco participates in a large ecosystem of partners, industry peers (yes, that includes competitors), and non-profits that provides insight and awareness into a multitude of security threats. We also have deep internal expertise. The Cisco Talos organization […]