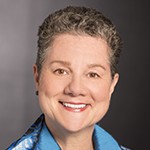
Edna Conway

Chief Security Officer
Chief Security Officer, Global Value Chain
Edna Conway serves as Cisco’s Chief Security Officer for its Global Value Chain. In this capacity, she develops and oversees the deployment of Cisco’s strategy to assess, monitor, and continuously improve the security and resiliency of its global value chain. Cisco's Value Chain Security Program spans its Supply Chain Operations, Engineering, Worldwide Partner and Services organizations. In addition, Conway drives Cisco’s supply chain cyber and security protection plan through its suppliers and channel partners. Conway serves or has served on the company’s Cyber-Security Board, Risk and Resiliency Operating Committee, Global Compliance Governance Committee and Eco Board. She also serves as a leader in various international security, supply chain, and sustainability standards, public-private partnerships, and information and communications industry consortia (e.g., ISO, iNEMI, IPC, The Open Group Trusted Technology Forum, The Common Criteria and the Electronics Industry Citizenship Coalition).Before joining Cisco’s Security and Trust Office, Conway has held multiple business, engineering and legal leadership positions at Cisco. Prior to Cisco, Conway was a partner in an international private legal practice and served as Assistant Attorney General for the State of New Hampshire.Recognized for her expertise across industries, Conway is a frequent speaker for many organizations and companies. Her speaking venues have included government, academic and industry forums. Her work has also been featured in a range of publications, analyst reports, and case studies, some of which are referenced at https://www.linkedin.com/in/ednaconwayShe holds an AB from Columbia University, a law degree from the University of Virginia and Executive Education credentials from Carnegie Mellon, New York and Stanford Universities and MIT.