As organizations adopt AI-enabled applications, cloud services, and hybrid work, branch offices have become critical access points to business data and operations—and attractive targets for cyberattacks.
Traditional security architectures designed for static networks can struggle to provide the visibility, performance, and control today’s distributed environments require. Modern branch security must protect users, applications, and data while remaining simple to deploy and manage across every location.
The Branch is Now the Front Line
Branches connect users, devices, cloud applications, and the internet. They also operate with limited on-site IT support, making centralized management and consistent security policies essential.
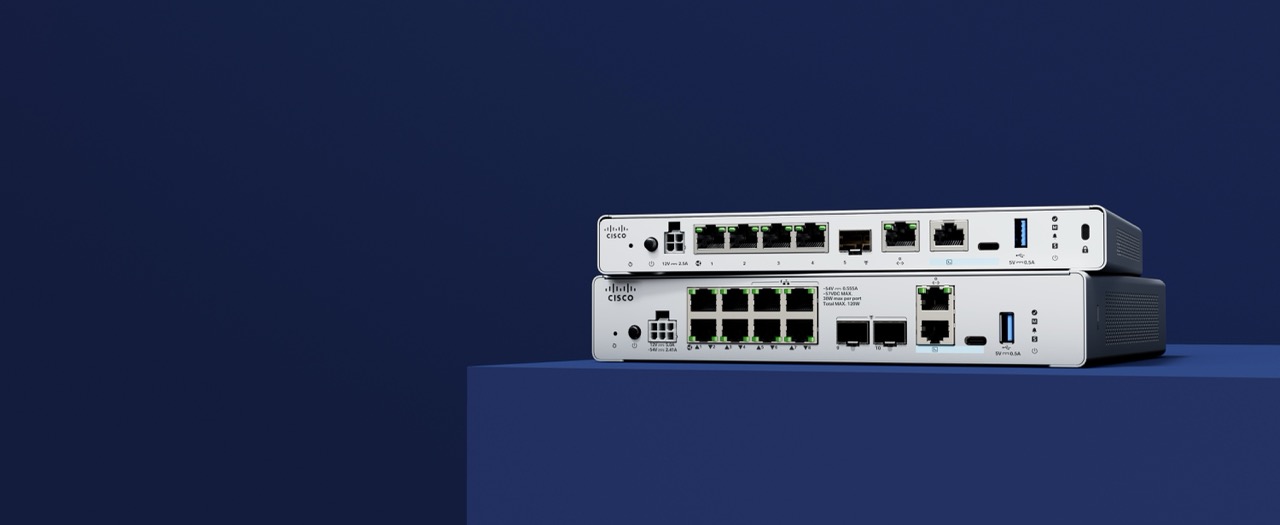
The Cisco Secure Firewall 200 Series brings enterprise-grade protection and connectivity to distributed branches in a compact form factor. It combines flexible software, intelligent threat detection, native SD-WAN capabilities, and centralized management to help organizations secure and simplify the modern edge.
Four Capabilities Modern Branches Need
- Visibility into encrypted traffic
Encryption protects legitimate business activity but can also conceal threats. The Encrypted Visibility Engine (EVE) uses AI and machine learning to analyze encrypted traffic, including TLS 1.3, without requiring full decryption. This helps identify and block potential threats while supporting performance and privacy requirements. - Protection against evolving attacks
Signature-based detection alone may not keep pace with rapidly changing attack techniques. SnortML extends Cisco’s Snort 3 intrusion prevention system with machine learning–based exploit detection, helping identify emerging threats and vulnerabilities before traditional signatures are available. - Secure, application-aware connectivity
The 200 Series integrates with Cisco SD-WAN to connect distributed sites securely and intelligently. Zero-Touch Provisioning (ZTP), reusable device templates, simplified branch-to-hub connectivity, Direct Internet Access (DIA), and dynamic path monitoring help organizations deploy branches consistently while supporting application performance and resilience. - Centralized visibility and control
Managing each branch individually increases operational effort and the risk of inconsistent policies. Cisco Cloud Control provides centralized visibility, policy management, and analytics across distributed firewall deployments. Its multitenant capabilities also help managed service providers (MSPs) manage multiple customer environments efficiently.
Built for Branch Performance
The 200 Series uses system-on-chip acceleration for encryption and traffic processing, helping support high-performance VPN, encrypted traffic analysis, and SD-WAN connectivity.
The Secure Firewall 220 model delivers up to 1.5 Gbps of throughput with next-generation firewall capabilities enabled in a compact form factor for smaller branches. The 240P provides a higher-capacity option with additional interfaces and integrated PoE+ support for more demanding deployments.
Secure the Modern Edge
AI, cloud adoption, and distributed work are changing what happens at the branch—and what organizations need to protect there. The Secure Firewall 200 Series helps meet these demands with intelligent threat protection, encrypted traffic visibility, resilient connectivity, and centralized management.
Whether deploying the 220 for smaller locations or the 240P for more demanding environments, organizations can strengthen branch security while simplifying operations.
Explore the Secure Firewall 200 Series to build a more resilient, manageable edge for the AI era.
Cisco Cybersecurity Viewpoints
Where security insights and innovation meet. Read the e-book, see the video, dive into the infographic and more…
Get expert perspectives now