How Cisco Cloud Control and Splunk Enterprise Security Unified Autonomous Threat Defense on Live Event Traffic
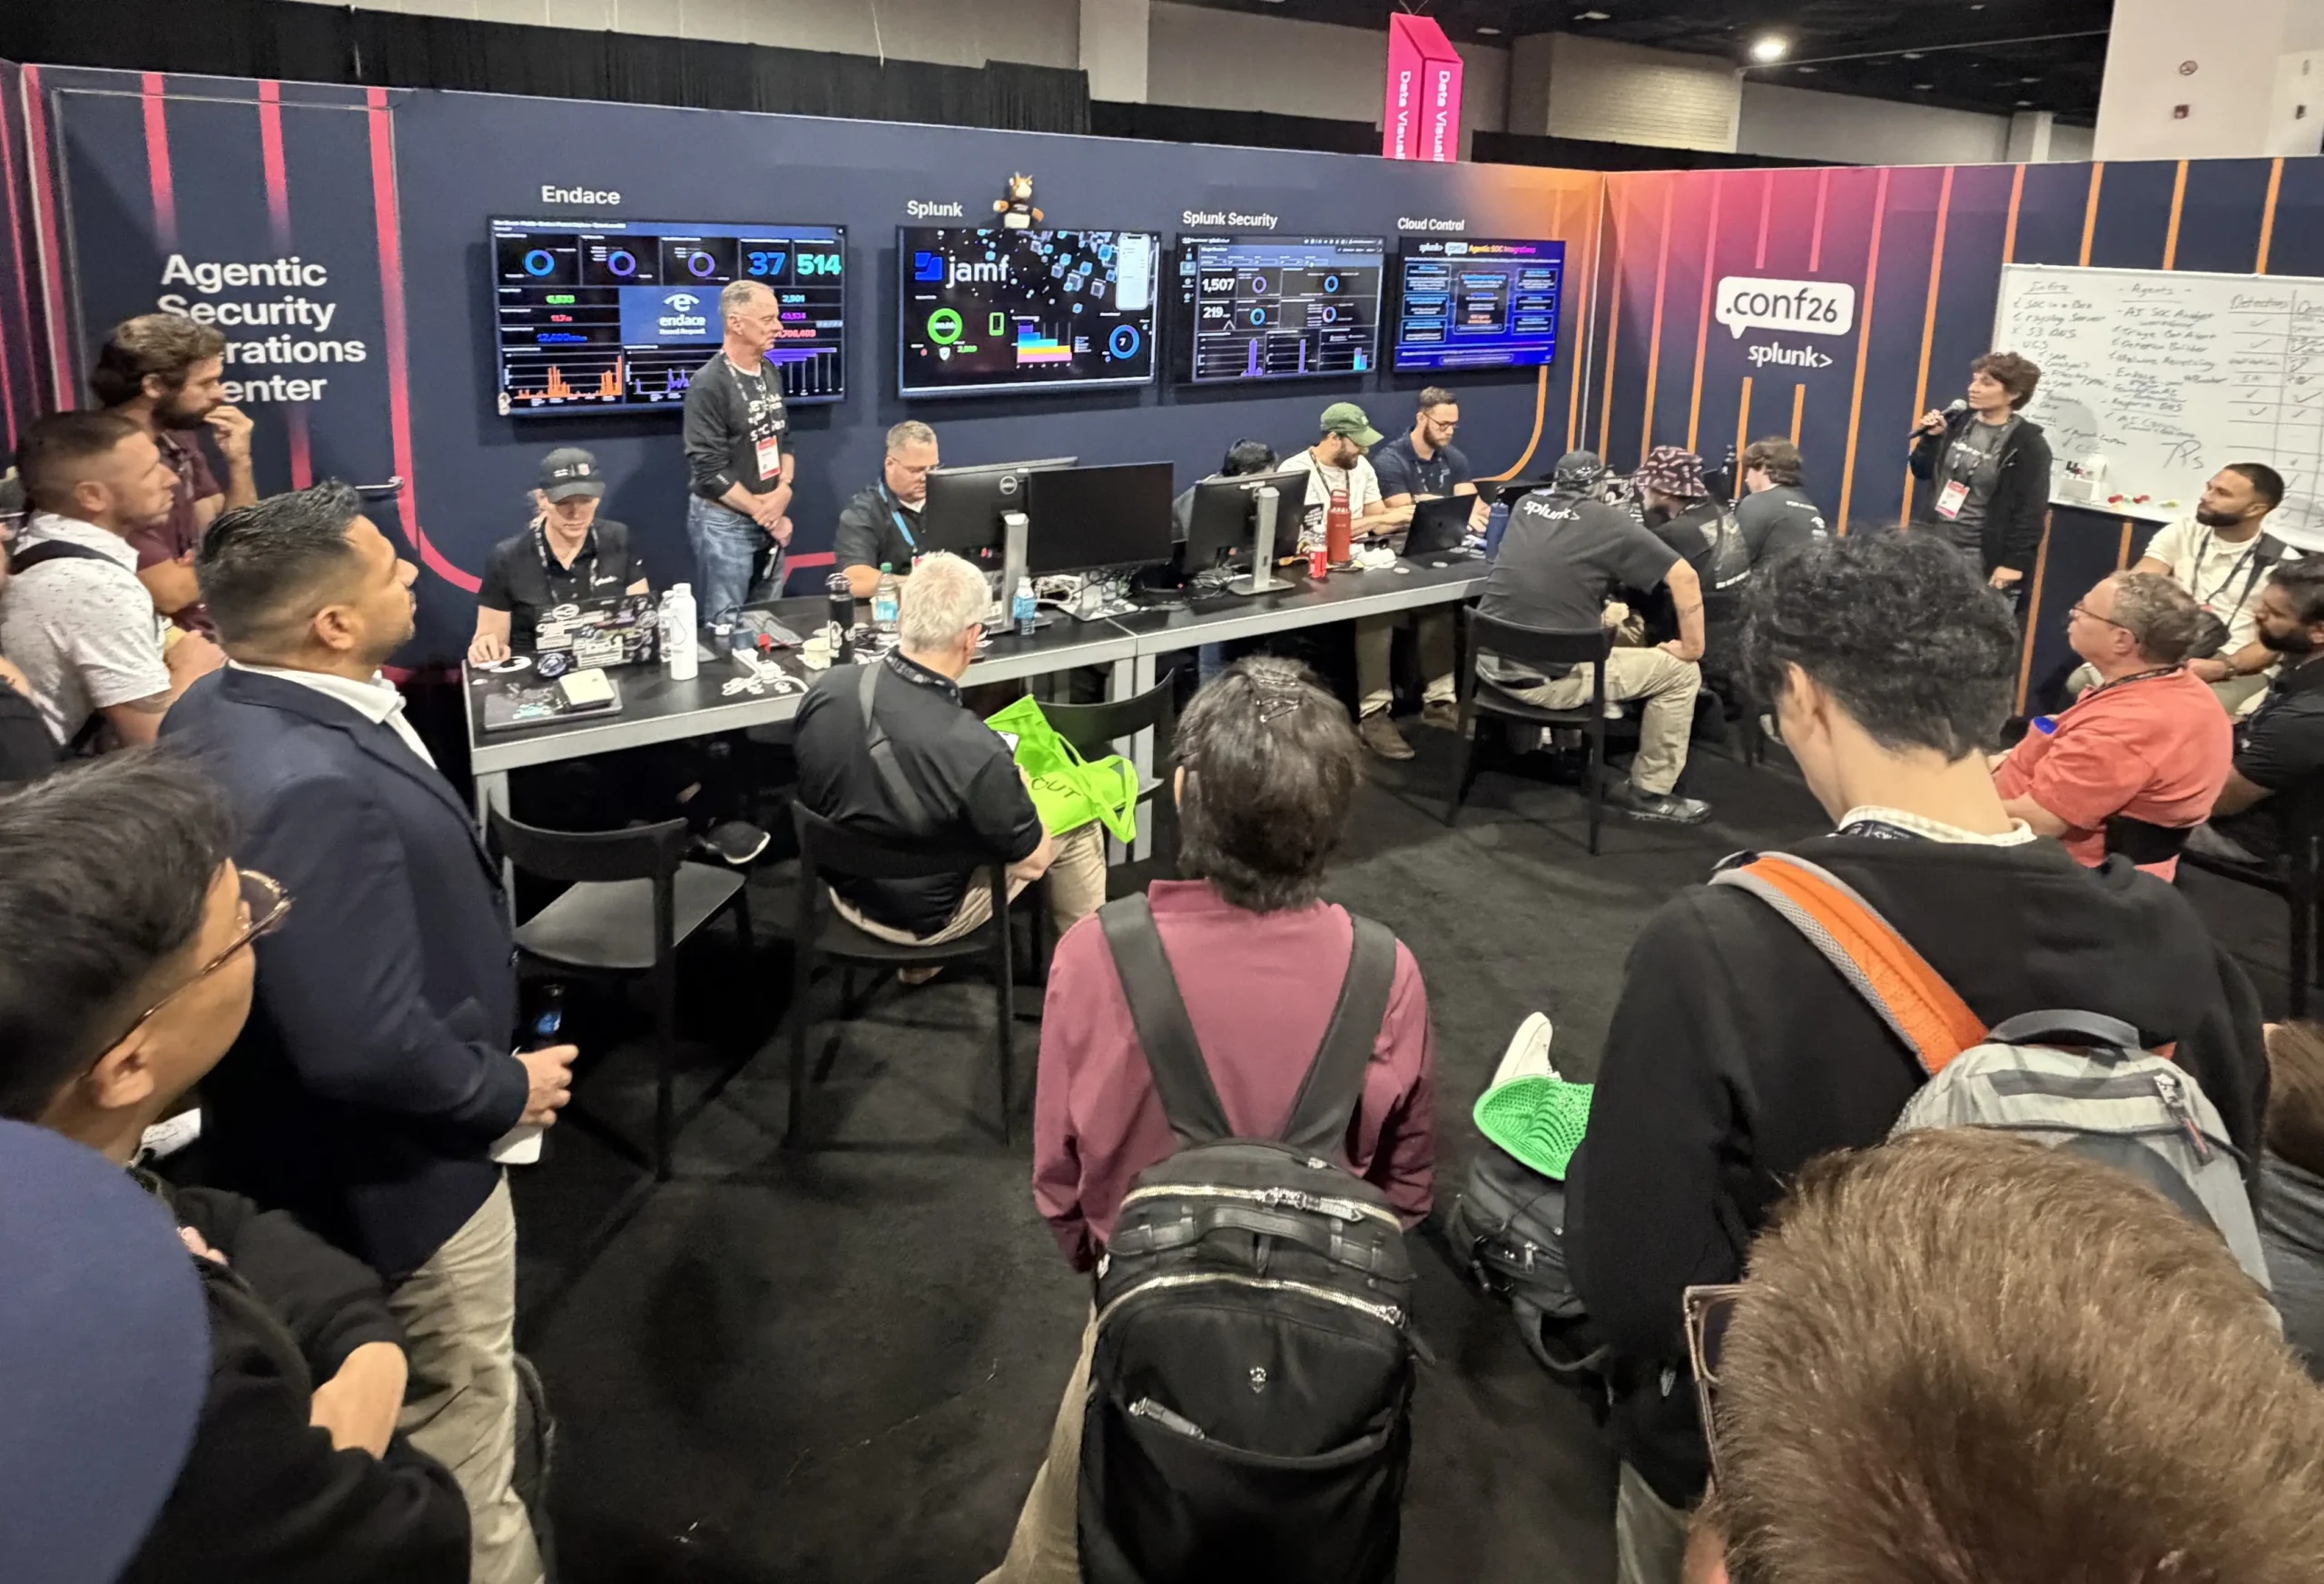
When Cisco and Splunk joined forces, the vision was to build a seamless, unified security architecture that eliminates the friction between the network, the endpoint, cloud workloads, and the security operations center. After battle testing at Black Hat USA, we turned that vision into operational reality at Splunk .conf26, by deploying an Agentic Security Operations Center (SOC) directly on the Pavilion floor.
Check out the retrospective video.
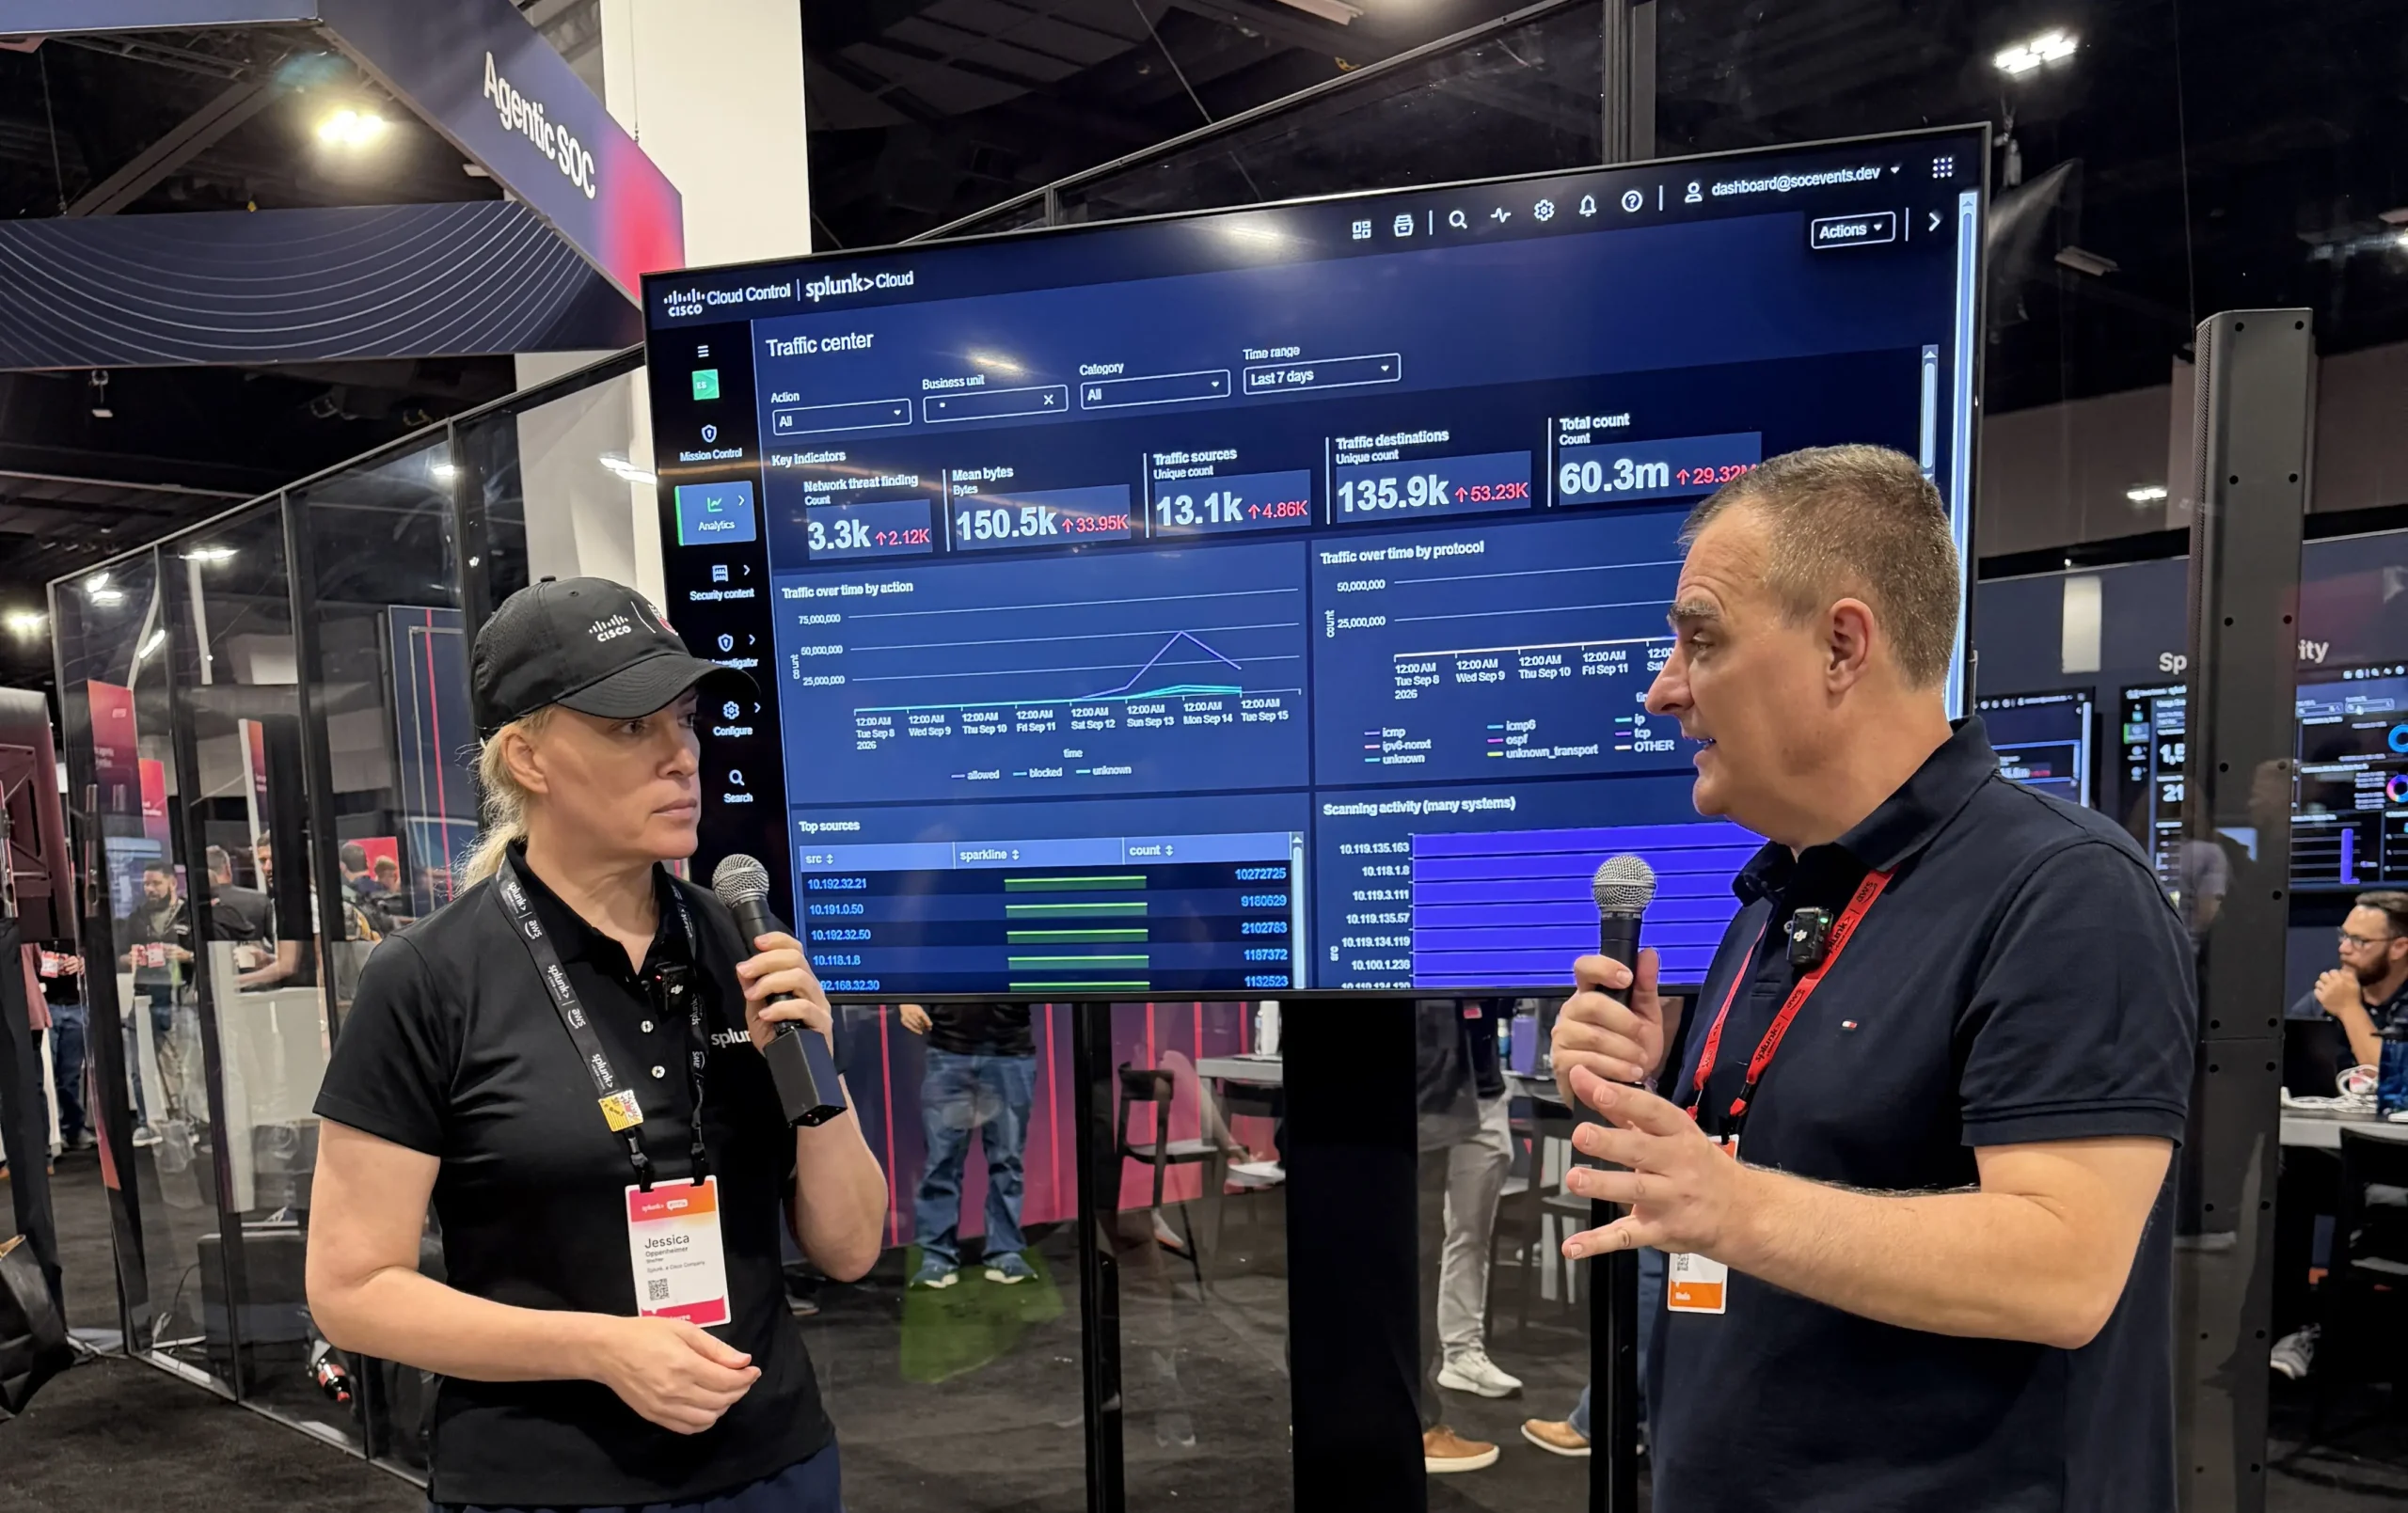
The .conf26 Agentic SOC was not a simulated demo or a scripted lab. It was a live security center actively protecting thousands of attendees, exhibitors, and venue network segments across the event. Powered by the Cisco Cloud Control management platform, Splunk Enterprise Security (ES), Cisco Security telemetry, Cisco Talos Intelligence, and Endace continuous packet capture, our joint team of Cisco, Splunk, Endace, and Jamf engineers demonstrated what multi-agent threat detection, investigation, and response (TDIR) delivers at enterprise scale. Watch it come to life in David Bombal’s Interview at the Agentic SOC.
The Mission: Protect First, Then Innovate in Public
The foundational mission of our event SOC is that the network must remain secure, and the attendee experience must be seamless. Event environments are among the most demanding proving grounds in cybersecurity. They are dynamic, high-throughput, and filled with thousands of unmanaged mobile devices, ephemeral workloads, and intentional security training and testing.
During .conf26, normal user behavior frequently was seen that would have been adversary traffic in corporate or government network, such as Splunk University training labs, Boss of the SOC (BOTS) competitions and live exploit demonstrations. Our core challenge was not simply generating alerts; it was discerning true malice from benign anomaly at line rate, without creating false-positive friction for attendees.
“The Agentic SOC is not about replacing human defenders with autonomous black boxes. It is about elevating the analyst, using specialized AI agents to shoulder the cognitive burden of multi-source correlation, log enrichment, and evidence gathering; while empowering human analysts to make governed, high-impact containment decisions.”
Cisco Cloud Control & Splunk ES: The Unified TDIR Architecture
Historically, SOC analysts have acted as the ‘human programming interface’—manually copying IP addresses, hash values, usernames, etc., between disconnected firewall consoles, DNS query logs, SIEM dashboards, and packet capture appliances. The One Cisco architecture dismantles these silos:
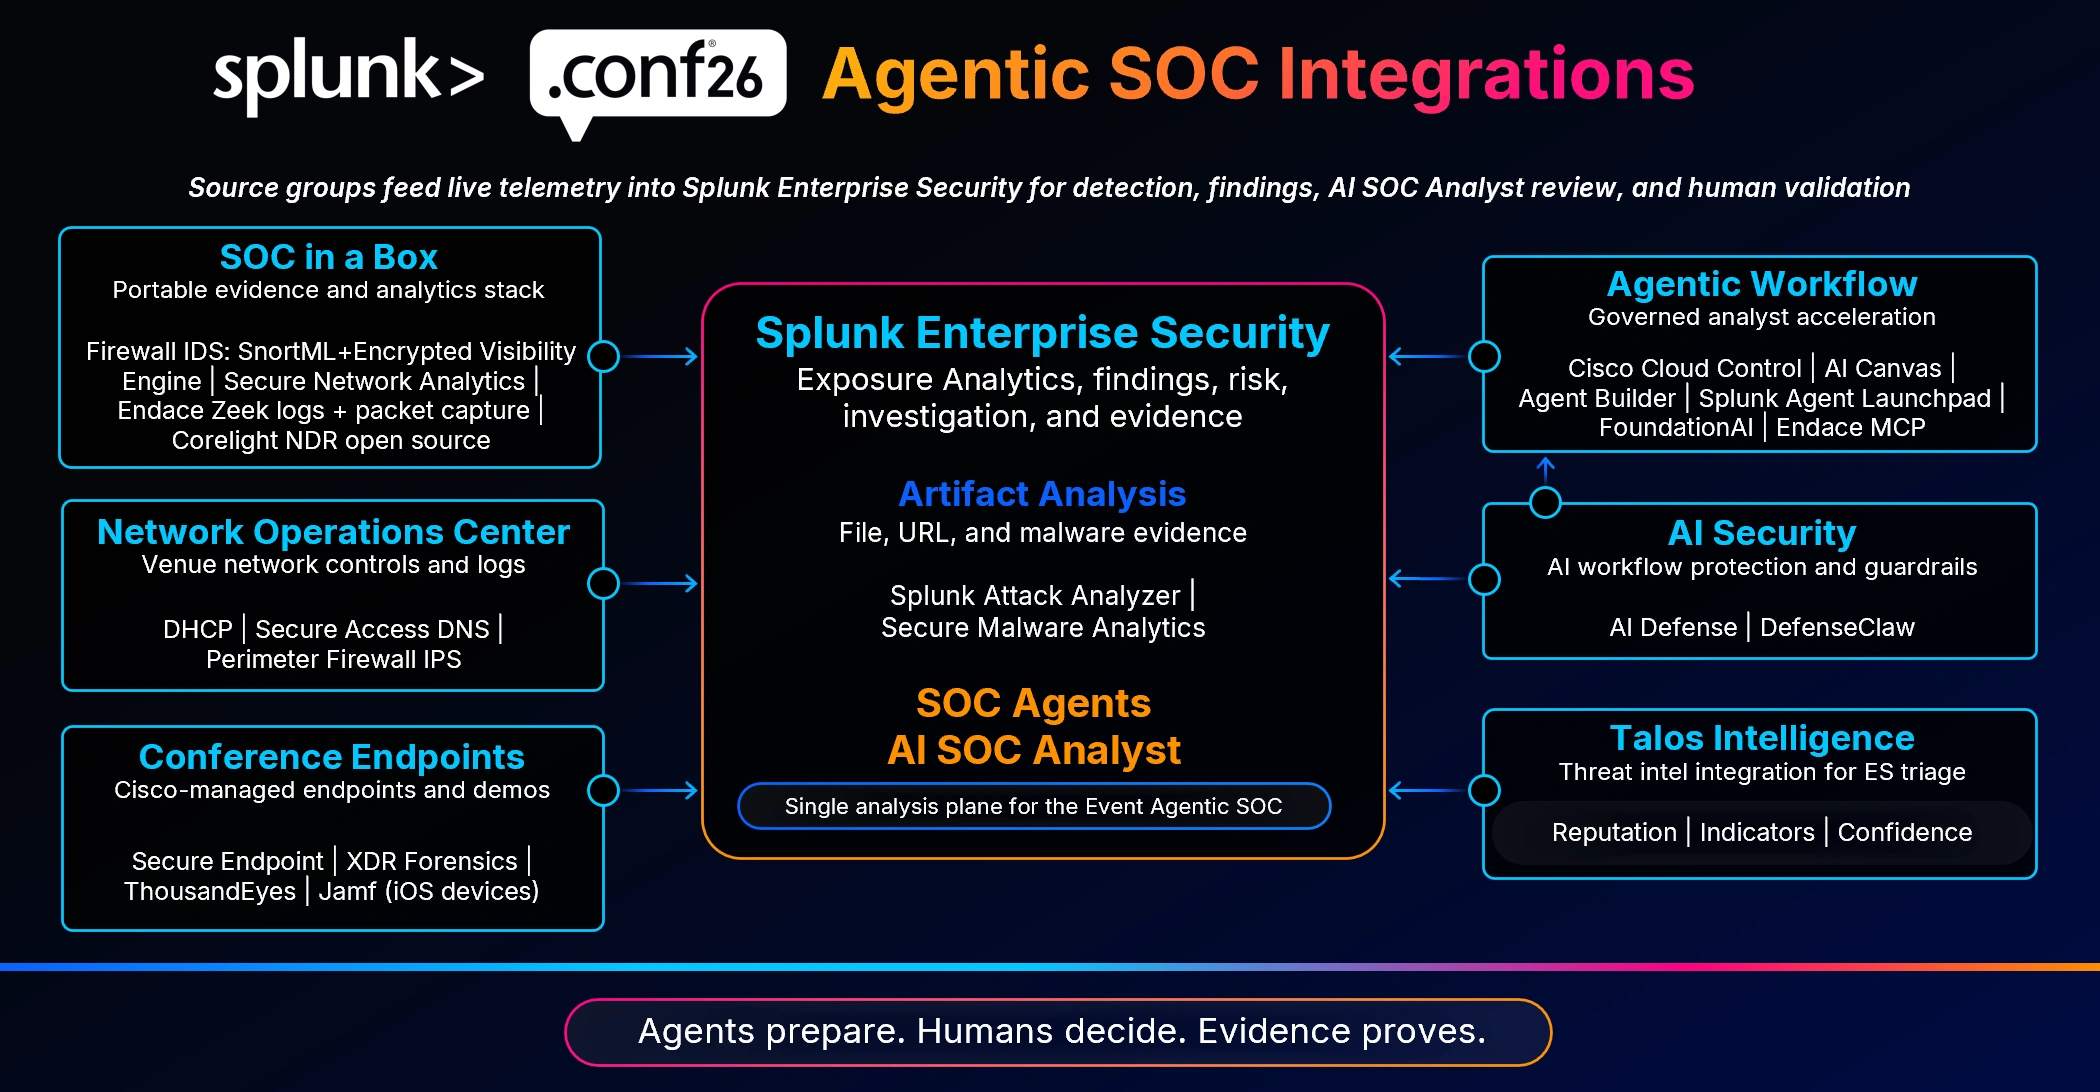
- Cisco Cloud Control as the Unified Control Plane: Serves as the central management engine connecting AI Canvas, Splunk Cloud, Cisco Secure Firewalls, Cisco Secure Access DNS telemetry, and network switching across the venue, streaming real-time telemetry directly into the analytics plane.
- Splunk ES as the TDIR Workbench: Aggregates Risk-Based Alerting (RBA) observables, correlation searches, and AI-driven Findings into a single, high-fidelity operational view.
- The Agentic SOC Workforce: Embedded AI agents (including the Splunk Triage Agent and Cisco AI Assistant) autonomously extract entity context, correlate related indicators of compromise (IOCs), summarize complex event sequences, and formulate structured response playbooks in seconds.
- Endace Continuous Packet Capture: Provides instant, deterministic ground truth—enabling one-click pivots from an AI triage finding directly into full packet streams for conclusive verification.
Frontline Case Study: From Autonomous Triage to On-Site Remediation
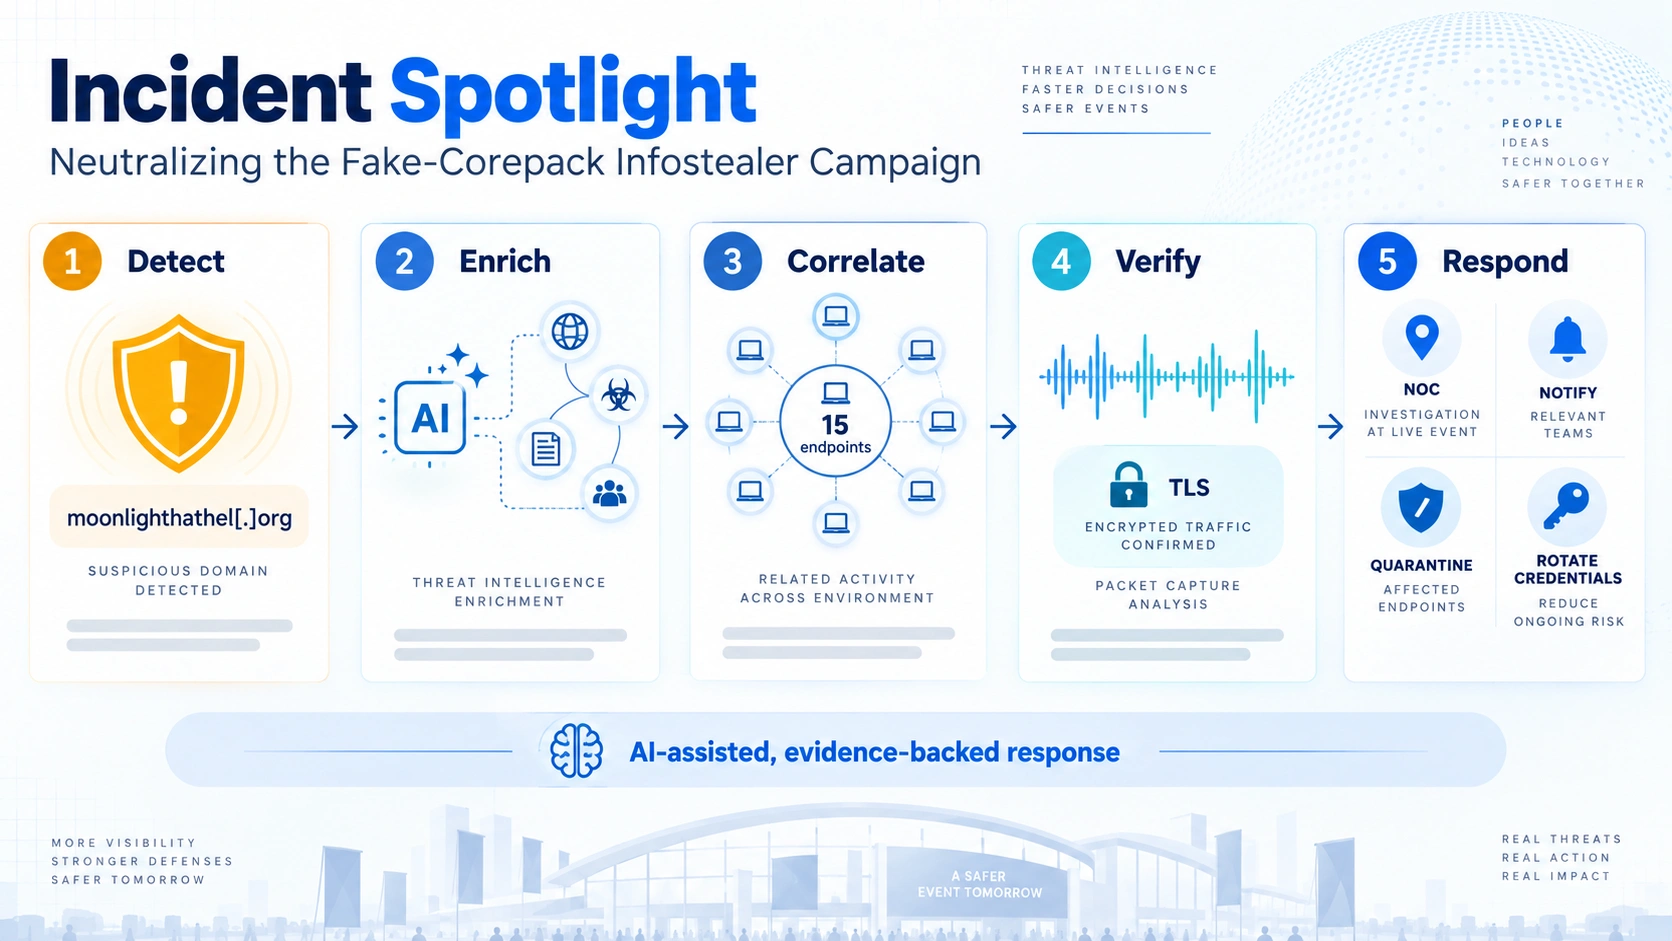
Incident Spotlight: Neutralizing the Fake-Corepack Infostealer Campaign
Within her first hour on the SOC floor, Oxana Sannikova, a Tier 1 analyst utilizing the ES Triage Agent, was alerted to an anomalous outbound connection to moonlighthathel[.]org. The AI agent instantly enriched the request with Cisco Talos threat intelligence, identifying the domain as an active command-and-control (C2) node in a widespread fake-Corepack npm credential-theft and proxyware campaign.
Tier 3 Incident Response lead Richard Marsh picked up the investigation. Rather than spending hours manually querying indexes, Richard received a complete correlation graph mapping the malware across 15 venue endpoints, using Endace packet capture integration to verify the encrypted C2 payload in flight.
Cross-referencing DHCP bindings and wireless access point telemetry, the NOC team physically located the attendee on the show floor. The attendee, a Splunk customer whose laptop had arrived on-site already compromised, was notified by their account manager, quarantined from the network, and guided through complete on-site remediation, credential rotation, and session invalidation.
The Power of One Cisco
The .conf26 Agentic SOC proved that when Cisco’s networking and security foundations unite with Splunk’s data analytics and TDIR engine. We do not just catch more threats, we transform the fundamental economics and operational speed of security teams. By automating triage with disciplined AI agents and backing every finding with verifiable network ground truth, we empower human analysts to defend modern enterprises with unprecedented confidence.
The analysts and engineers wrote about their experiences in these blog posts.
- The Queue Is a Graph, Not a To-Do List
- Trusted Agentic SOC: The AI in Security and the Security in AI
- A Network Engineer Walks into the Agentic SOC: What AI Taught Me About Security Operations
- Scalpel Versus Sledgehammer
- Tracking the Triage Agent in the Agentic SOC at Splunk .conf26
- The Zero-Day Blind Spot: Why Your Agentic SOC needs Retrospective Packet Replay
- Chasing AMMYY at Splunk .conf
- Admin in the Loop: Firewalls and the Agentic SOC
- From Novice to Senior – How an MCP-Enabled Capture Appliance Changes Threat Hunting
- Decode First, Panic Later: A Tier 3 Analyst’s Case for Staying in the Loop
- Endace: Why Full Packet Capture Becomes Mission-Critical in the Agentic SOC
- Endace: Richer Data for the Agentic SOC
- Endace: Letting the Agentic SOC Handle the Drudgery So the Humans Can Dig Deeper
We look forward to seeing you at Cisco Live APJC in Melbourne, Black Hat Europe, Cisco Live EMEA in London, and RSAC in San Francisco!
Acknowledgements
Our thanks to the engineers who built the Agentic SOC and the Humans who provided decision making expertise.
- SOC Co-Leader Architecture: Paul Pelletier
- Agentic SOC Innovation: Ryan Maclennan & Aditya Sankar
- Splunk Integrations: Josh Wilson & Christian Cloutier
- SOC Analysts: Christopher Van Der Made, Sean Clapper, Oxana Sannikova, Daniel Christiansen, Lily Lee, Dan Burke, Kyle Vaughan & Ray Aragon
- Cisco Security Firewall / Switching: Adam Kilgore & Andrew Merica
- SOC VIP Tours Coordinator/Ops: Michelle Hermosillo
- Threat Hunter Tier 3/IR: Richard Marsh & Allison Gallo
- Detection Engineer: Rod Soto
- AI Canvas / XDR Forensics: Rob Gresham
- AI SOC Analyst Engineering: Fred Frey
- Remote support: Bhavin Patel, Shyue Hong Chuang, Nasreddine Bencherchali, Onur Erdogan, Nathan Schoen, Paul Carrillo, Jon Lane, Ryan Stillions & Raven Tait
- Endace Full Packet Capture: Michael Morris, Tom Leahy, Anantha Srinivasan, Elliott Hinson & Andreas Lof
- Jamf proof of value: Adam Derrick
Cisco Cybersecurity Viewpoints
Where security insights and innovation meet. Read the e-book, see the video, dive into the infographic and more…
Get expert perspectives now