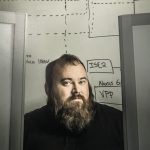
Craig Williams has always had a passion for learning how things operate – and circumvent security measures. His deep interest in security technology led to a career at Cisco, which began with research into vulnerabilities, threats, and network detection techniques. His research over the past decade has included running the Cisco malware lab and trying to outwit the very security products he has helped Cisco to design.
New areas of network protection, including the utilization of new evasion techniques and threats, have emerged directly from Mr. Williams’ work. Today, as a Director of the Talos Outreach team, Mr. Williams is focused on building next-generation security products covering web and email security, threat defense systems, and security management systems. Through his work and involvement with Cisco Talos – Outreach, he looks to give back to the Internet and security community by helping to bring attention to the breadth and depth of Cisco’s threat research.
Mr. Williams is also working to extend Cisco’s threat defense technologies to a wider range of networking products, broadening the controls and countermeasures that are utilized by existing technologies, and extending coverage across more protocols. His expertise includes designing IPS/IDS signatures, penetration testing, reverse engineering, vulnerability research, botnets, and attack obfuscation.
As Director of the Talos – Outreach team, Craig helps to guide some of the most experienced and knowledgeable threat researchers and analysts at Cisco – and in the industry. Their collaborative research and analysis work is intended not only to continually enhance the quality and efficacy of Cisco’s security products, but also, provide actionable intelligence that helps all Internet users defend against both known and emerging network threats.
Previous roles
Before joining the Cisco Talos – Outreach team, Mr. Williams was Technical Leader for Signature Engineering at Cisco Security Research and Operations (SRO) at Cisco Security Intelligence Operations (SIO), a role he held for two years. He examined trends for research projects, and provided guidance regarding vulnerability research, inspection enhancements, and areas for future development. From 2008-2011, he was a founding member of Cisco’s Applied Security Research team, where he focused on botnets and botnet mitigation.
More about Craig Williams …
Among Mr. Williams’ significant contributions to Cisco is an issued patent, “enhanced server to client session inspection,” which involves obfuscated traffic inspection.
He is also the proud recipient of a Google “Bug Bounty,” which he earned by figuring out how to download paid digital content for free from the Google Play Store – and swiftly alerting Google to the problem. (A very tired but elated Mr. Williams made the discovery around 3 a.m., just hours after bringing home his newborn daughter from the hospital.) He earned a subsequent Google bug bounty for discovering an issue around whois information for google apps customers. This is documented here.
Mr. Williams holds a Bachelor’s degree in Computer Science from The University of Texas at Austin.
Cisco Talos – Outreach
Through research projects, publications, presentations, and other front-facing activities, the expert threat researchers and analysts on the Cisco Talos – Outreach team help Cisco customers, the security community, industry, and the public understand the value of Cisco CSI and the early-warning intelligence, threat, and vulnerability analysis its researchers provide.
Additionally, the Cisco Talos – Outreach team, works with media outlets to provide timely, in-depth insight and analysis on major web security incidents. Cisco Talos – Outreach team members are also regular contributors to Cisco Security Reports and the Cisco Security Blog.