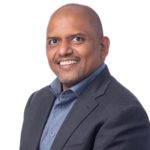
Ravi Chandrasekaran
Senior Vice President, Engineering
Catalyst Engineering Group
Ravi Chandra is responsible for product development across Cisco's switching, routing, wireless, IoT, network automation and analytics portfolios. He leads the engineering effort on the Cisco Digital Network Architecture (DNA).
Previously at Cisco, Chandra served as Vice President of Software for the Enterprise Networking Group, where he created a cohesive software-plus-services architecture for the enterprise market segment. Before that, he was Vice President and General Manager of the Services Routing Group when it delivered Cisco's flagship WAN edge router and WAN Optimization platforms as well as products for the Cloud Intelligent Network. He also spent the first part of his career at Cisco, where he developed a significant part of the Cisco BGP and MPLS forwarding protocols and co-authored six RFCs.
Before rejoining Cisco, Chandra was co-founder and Vice President of Products at Apigee, a provider of API technology and services for enterprise businesses and developers. Apigee was recently acquired by Google. Earlier still, he was the Senior Vice President of Engineering at Redback Networks, responsible for all of their research and development. There he architected the software for the SmartEdge Service Gateway, a subscriber management and edge routing platform.
Chandra holds a Bachelor of Science degree in electrical engineering from Anna University, Chennai, India, and a Master of Science degree in communications engineering from the University of Missouri, Kansas City.